
CSPM Solution in Europe for Cloud Security Visibility
As European organizations accelerate cloud adoption across AWS, Azure, and GCP, cloud misconfigurations have emerged as one of the fastest-growing causes of security breaches — and one of the hardest to manage at scale.
Every undetected misconfiguration becomes a potential entry point for attackers — driving unauthorized access, data breaches, and compliance violations that carry severe regulatory consequences.
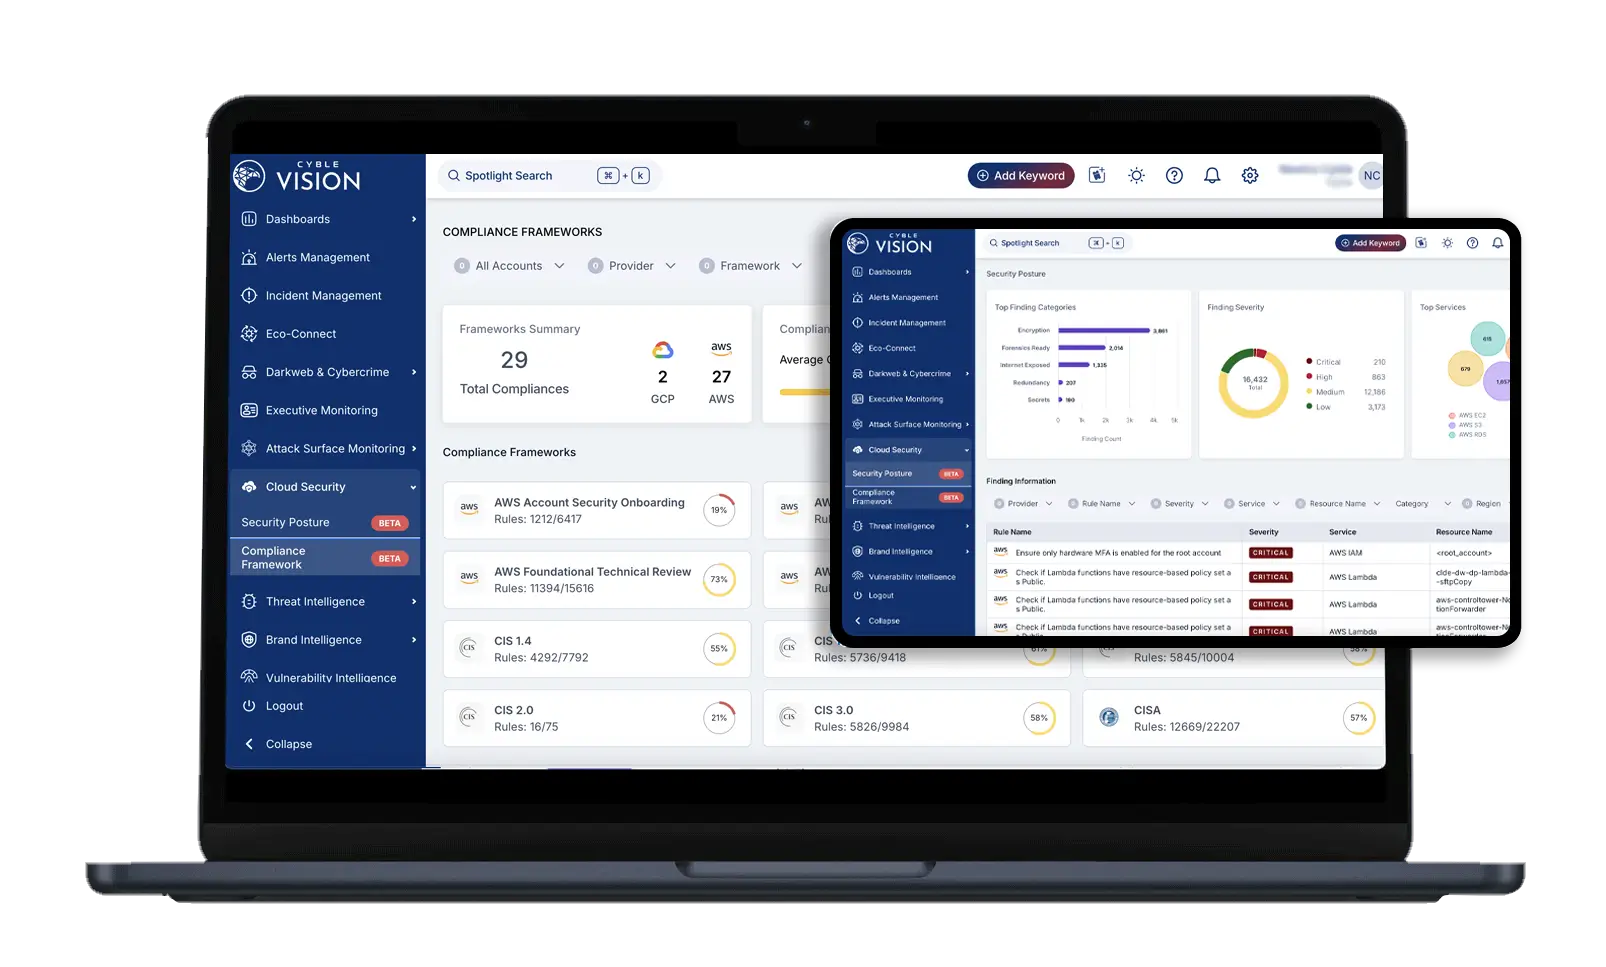
Cyble delivers advanced Cloud Security Posture Management (CSPM) Solutions in Europe through its unified Cloud Security Platform, providing continuous, real-time visibility into cloud misconfigurations, compliance violations, and security drift — helping European organizations prioritize remediation and maintain audit-ready cloud posture.
Why European Organizations Need CSPM Solutions
With increasing regulatory scrutiny under NIS2, GDPR, and sector-specific mandates, cloud configuration visibility and continuous compliance are no longer optional.
Cyble’s CSPM platform helps European organizations:
Continuously monitor cloud configurations across AWS, Azure, and GCP
Detect misconfigurations before attackers exploit them
Map cloud resources against 50+ compliance frameworks automatically
Track and audit configuration changes in real time
Reduce human error — a leading factor in cloud data breaches
Strengthen compliance posture with European regulatory frameworks
Improve cyber resilience through continuous cloud intelligence
Cyble transforms cloud complexity into actionable configuration security clarity.
The Current Cloud Misconfiguration Threat Landscape in Europe
Attackers increasingly exploit cloud misconfigurations as the fastest path into enterprise cloud environments.
The cloud security landscape continues to intensify:

0
%
Rise in cloud security incidents recorded in 2024 
0
%
Of companies experienced at least one cloud breach in the past year 
0
%
Of organizations affected by misconfigured or unpatched cloud systems 
0
%
Of breaches stemmed directly from cloud misconfigurations 
0
%
Of initial breach vectors traced to cloud misconfigurations (3rd most common)Without continuous monitoring, European organizations remain blind to critical misconfigurations that exist outside point-in-time audit cycles.
Key Features of Cyble’s CSPM Platform
Real-Time Cloud Configuration Monitoring
Continuous visibility every 60 minutes across AWS, Azure, and GCP — detecting misconfigurations before they are exploited.
50+ Compliance Framework Coverage
Automated mapping against CIS Benchmarks, PCI-DSS, NIST, ISO/IEC 27001, GDPR, HIPAA, FedRAMP, NIS2, SOC2, MITRE ATT&CK, and more.
Automated Compliance Checks:
Continuous, automated validation across 33 AWS frameworks, 8 Azure frameworks, and 8 GCP frameworks — replacing labor-intensive manual audits.
Security Drift Detection
Identify unauthorized changes and configuration drift in real time to prevent prolonged exposure.
Audit Trail & Change Control
Track and monitor the full history of cloud configuration changes — ready for regulatory audits at any time.
Cloud Security Posture Scoring
Actionable, risk-prioritized scoring with guided remediation steps so security teams focus on what matters most.
Multi-Cloud Asset Inventory
Maintain a real-time, dynamic inventory of cloud resources across all cloud providers from a single pane of glass.
Recognized By Global Analyst Firms
Analysts from major research houses, industry critics, and cybersecurity leaders across the globe admire Cyble Vision’s capabilities.
-
Cyble Recognized in the Gartner® Hype Cycle™ for Cyber-Risk Management, 2025 -
Cyble Named Sample Vendor in Gartner® Hype Cycle™ for Security Operations 2025 -
Cyble Named a Sample Vendor in Gartner® Hype Cycle™ for Managed IT Services 2025 -
Cyble Recognized in Gartner Emerging Tech 2025 Report -
Cyble Recognized in Gartner Hype Cycle for Cyber Risk Management 2024 -
Cyble Recognized in Gartner Hype Cycle for Digital Risk Protection, 2024 -
Cyble Recognized in Gartner Hype Cycle for Managed IT Services, 2024

-
Cyble Recognized in Forrester’s Threat Intelligence Service Providers Landscape 2025 Report -
Cyble Recognized among notable vendors in Forrester’s report on Attack Surface Management (ASM) providers.

-
Cyble Recognized in SPARK Matrix 2025 Digital Threat Intelligence Report
Resources








FAQs About CSPM Solutions in Europe
What are CSPM solutions in Europe and how does Cyble help?
CSPM solutions are security tools and processes that help organizations ensure the safety and compliance of their cloud environments by automating detection of misconfigurations and identifying compliance issues. Cyble serves European organizations with a CSPM solution that offers a comprehensive toolset for managing cloud assets, meeting compliance standards, and proactively identifying vulnerabilities — seamlessly integrated with CybleVision and CybleHawk for unified threat detection.
How does Cyble provide Cloud Security Posture Management solution in Europe?
Cyble’s CSPM solution monitors cloud environments in real time, identifying misconfigurations, vulnerabilities, and policy drift, while automatically assessing configurations against frameworks such as GDPR, HIPAA, and PCI-DSS with audit-ready reporting.
What Cloud Security Posture Management tools does Cyble offer in Europe?
Cyble’s CSPM tools provide instant, full visibility into cloud assets across multiple providers, detect misconfigurations without intrusive agents (integrated with Attack Surface Management), and offer continuous compliance monitoring across AWS, Google Cloud, and other platforms through a single unified interface.
What are CSPM tool in Europe and how does Cyble differentiate?
CSPM tools in Europe are automated solutions that continuously monitor cloud environments for misconfigurations, compliance violations, and security risks. Cyble differentiates by combining CSPM with deep threat intelligence. Unlike standard tools, Cyble’s CSPM integrates with Cyble Vision delivering unified threat detection, real-time compliance, and automated risk management across both cloud and on-premises environments. It also supports agentless deployment, integrates with SIEM/SOAR platforms, and scales across AWS, Azure, GCP, hybrid, and multi-cloud setups— making it a uniquely intelligence-first CSPM solution for European enterprises.
Who are the leading CSPM vendors in Europe and where does Cyble fit?
Cyble has been recognized in the Gartner® Hype Cycle™ for Cyber-Risk Management and Managed IT Services, positioning it among notable vendors globally. Cyble differentiates itself by integrating CSPM with CybleVision, delivering unified threat detection, real-time compliance, and automated risk management — going beyond risk identification to provide a holistic cloud security approach.
How does Cyble support Cloud Security Posture Management in Europe?
Cyble’s CSPM system supports European enterprises by simplifying regulatory compliance with GDPR, HIPAA, and SOC 2, offering tailored security policies, and providing consistent protection across AWS, Microsoft Azure, and Google Cloud.
Which industries in Europe benefit from Cyble’s CSPM in Europe?
Industries such as finance, healthcare, and government benefit most, as Cyble’s CSPM automates compliance with GDPR, HIPAA, and PCI-DSS — enabling real-time monitoring, risk mitigation, and comprehensive audit reporting critical to regulated sectors.
How do Cyble’s CSPM tools improve cloud security in Europe?
Cyble’s tools detect risky cloud settings such as public buckets, overly permissive IAM roles, and unsafe network rules, then prioritize remediation using intelligence-backed risk scoring — helping European enterprises reduce their attack surface, maintain compliance, and respond to threats faster.
What are Cyble’s incident management products in Europe?
Cyble’s incident management product suite includes its AI-powered threat detection engine, automated playbook execution, multi-source alert correlation, and a centralized incident dashboard. Together, these products give European SOC teams a structured, intelligence-driven approach to managing security incidents at scale.
Why choose Cyble for incident management solutions in Europe?
Cyble combines deep threat intelligence heritage with automated incident response capabilities purpose-built for the European regulatory environment. Its platform covers GDPR, NIS2, and sector-specific compliance frameworks — giving organizations both the operational efficiency and audit-ready documentation needed to manage incidents confidently.
How do Cyble’s incident management tools improve SOC operations?
Cyble reduces manual workload by automating alert triage, correlation, and response playbooks — allowing SOC analysts to focus on high-priority threats. Its risk-prioritized incident scoring ensures teams address the most critical incidents first, improving response times and overall SOC efficiency.
Are Cyble’s incident management services compliant with European regulations?
Yes. Cyble’s incident management services are aligned with GDPR, NIS2, ISO/IEC 27001, and PCI-DSS requirements. The platform generates audit-ready incident reports and maintains complete investigation trails, helping European organizations demonstrate compliance to regulators with minimal additional effort.
How does Cyble support real-time incident response in Europe?
Cyble enables real-time incident response through continuous monitoring, instant alert generation, and automated response workflows that trigger the moment a threat is detected. Its platform aggregates signals across endpoints, cloud environments, and network layers — giving European teams the context needed to act decisively and immediately.
What industries in Europe use Cyble’s incident management solutions?
Cyble’s incident management solutions serve financial services, healthcare, critical infrastructure, retail, public sector, and technology organizations across Europe. Regulated industries particularly benefit from Cyble’s compliance-aligned reporting and automated workflows that address sector-specific mandates such as DORA, NIS2, GDPR, and PCI-DSS.
How do Cyble’s incident management products reduce alert fatigue?
Cyble reduces alert fatigue by applying AI-driven correlation and risk prioritization to filter out noise and surface only the most actionable incidents. By consolidating alerts from multiple sources into a unified, context-enriched view, Cyble ensures analysts spend time on real threats rather than chasing false positives.
CSPM solutions are security tools and processes that help organizations ensure the safety and compliance of their cloud environments by automating detection of misconfigurations and identifying compliance issues. Cyble serves European organizations with a CSPM solution that offers a comprehensive toolset for managing cloud assets, meeting compliance standards, and proactively identifying vulnerabilities — seamlessly integrated with CybleVision and CybleHawk for unified threat detection.Cyble’s CSPM solution monitors cloud environments in real time, identifying misconfigurations, vulnerabilities, and policy drift, while automatically assessing configurations against frameworks such as GDPR, HIPAA, and PCI-DSS with audit-ready reporting.Cyble’s CSPM tools provide instant, full visibility into cloud assets across multiple providers, detect misconfigurations without intrusive agents (integrated with Attack Surface Management), and offer continuous compliance monitoring across AWS, Google Cloud, and other platforms through a single unified interface.CSPM tools in Europe are automated solutions that continuously monitor cloud environments for misconfigurations, compliance violations, and security risks. Cyble differentiates by combining CSPM with deep threat intelligence. Unlike standard tools, Cyble’s CSPM integrates with Cyble Vision delivering unified threat detection, real-time compliance, and automated risk management across both cloud and on-premises environments. It also supports agentless deployment, integrates with SIEM/SOAR platforms, and scales across AWS, Azure, GCP, hybrid, and multi-cloud setups— making it a uniquely intelligence-first CSPM solution for European enterprises.Cyble has been recognized in the Gartner® Hype Cycle™ for Cyber-Risk Management and Managed IT Services, positioning it among notable vendors globally. Cyble differentiates itself by integrating CSPM with CybleVision, delivering unified threat detection, real-time compliance, and automated risk management — going beyond risk identification to provide a holistic cloud security approach. Cyble’s CSPM system supports European enterprises by simplifying regulatory compliance with GDPR, HIPAA, and SOC 2, offering tailored security policies, and providing consistent protection across AWS, Microsoft Azure, and Google Cloud. Industries such as finance, healthcare, and government benefit most, as Cyble’s CSPM automates compliance with GDPR, HIPAA, and PCI-DSS — enabling real-time monitoring, risk mitigation, and comprehensive audit reporting critical to regulated sectors.Cyble’s tools detect risky cloud settings such as public buckets, overly permissive IAM roles, and unsafe network rules, then prioritize remediation using intelligence-backed risk scoring — helping European enterprises reduce their attack surface, maintain compliance, and respond to threats faster.Cyble’s incident management product suite includes its AI-powered threat detection engine, automated playbook execution, multi-source alert correlation, and a centralized incident dashboard. Together, these products give European SOC teams a structured, intelligence-driven approach to managing security incidents at scale. Cyble combines deep threat intelligence heritage with automated incident response capabilities purpose-built for the European regulatory environment. Its platform covers GDPR, NIS2, and sector-specific compliance frameworks — giving organizations both the operational efficiency and audit-ready documentation needed to manage incidents confidently. Cyble reduces manual workload by automating alert triage, correlation, and response playbooks — allowing SOC analysts to focus on high-priority threats. Its risk-prioritized incident scoring ensures teams address the most critical incidents first, improving response times and overall SOC efficiency. Yes. Cyble’s incident management services are aligned with GDPR, NIS2, ISO/IEC 27001, and PCI-DSS requirements. The platform generates audit-ready incident reports and maintains complete investigation trails, helping European organizations demonstrate compliance to regulators with minimal additional effort. Cyble enables real-time incident response through continuous monitoring, instant alert generation, and automated response workflows that trigger the moment a threat is detected. Its platform aggregates signals across endpoints, cloud environments, and network layers — giving European teams the context needed to act decisively and immediately. Cyble’s incident management solutions serve financial services, healthcare, critical infrastructure, retail, public sector, and technology organizations across Europe. Regulated industries particularly benefit from Cyble’s compliance-aligned reporting and automated workflows that address sector-specific mandates such as DORA, NIS2, GDPR, and PCI-DSS. Cyble reduces alert fatigue by applying AI-driven correlation and risk prioritization to filter out noise and surface only the most actionable incidents. By consolidating alerts from multiple sources into a unified, context-enriched view, Cyble ensures analysts spend time on real threats rather than chasing false positives.
Schedule a Personalized Demo
Gain real-time visibility into your cloud misconfigurations and prioritize remediation before attackers exploit them.
Book your demo today