
AI-Powered Threat Intelligence Platform for Proactive Defense
Cyble Cyber Threat Intelligence Platform provide holistic visibility into emerging threats and adversary activity. Discover, prioritize, and respond to risks faster with built-in analytics and automation that strengthen resilience.
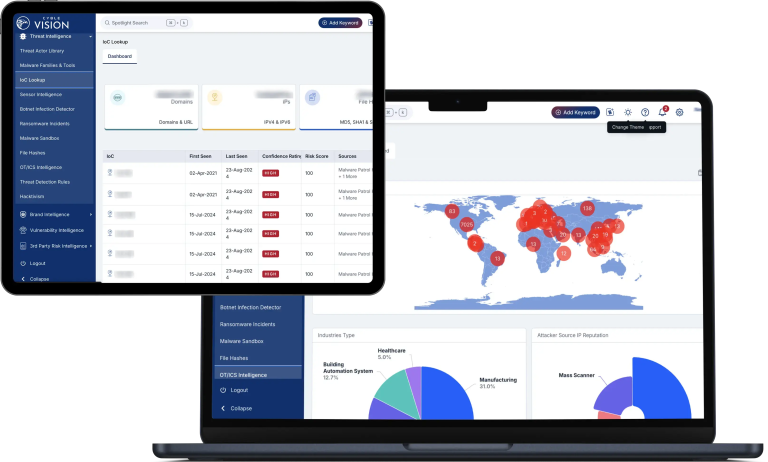
What Powers Cyble Threat Intelligence
- 200B+ Dark Web Records
- 98.5% Takedown Success Rate
- Gartner MQ 2026 Challenger
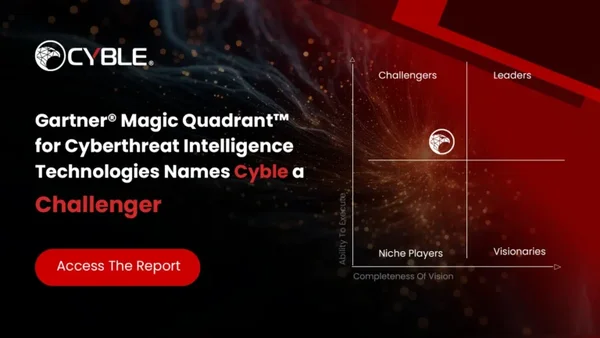
Cyble Named a Challenger in the 2026 Gartner® Magic Quadrant™ for Cyberthreat Intelligence Technologies
Capabilities unified in one AI-native platform
Customers protected across 50+ countries
Alert parameters to tune notifications to your organization
Threat data points tracked across the surface, deep, and dark web
What is Cyble Threat Intelligence Solution?
The Cyble Threat Intelligence Solution provide an end-to-end view of the evolving threat landscape, empowering organizations to anticipate, detect, and mitigate risks faster. Built with advanced analytics, automation, and AI-driven insights, this unified cyber threat intelligence solution suite enables security teams to act before incidents occur.
By collecting data from the surface, deep, and dark web, the platform delivers real-time intelligence on emerging threats, vulnerabilities, and threat actors. Cyble’s cyber security threat intelligence approach helps enterprises, governments, and critical sectors strengthen resilience and make informed, proactive security decisions.
Threat Data Points

Cyble Wins Gold at Cybersecurity Excellence Awards for Threat Intelligence

Cyble Named a Leader in QKS Group’s 2025 SPARK Matrix™ for Digital Threat Intelligence Management

Cyble Recognized in Forrester's External Threat Intelligence Service Providers Landscape, Q1 2026 report
AI-Powered Threat Intelligence That Turns Signals Into Proactive Defense
See the bigger picture. Cyble publishes threat landscape reports across regions, including North America, Europe, APAC, and the Middle East, giving security leaders the context to assess risk and guide strategy.
Know who is targeting you and how. Cyble monitors cybercrime forums, ransomware leak sites, and encrypted channels to surface threat actor discussions, initial access offers, planned attacks, and stolen data linked to your organization.
Understand how attackers operate. Cyble maps adversary tactics, techniques, and procedures to MITRE ATT&CK, helping threat hunters and SOC analysts spot patterns and strengthen detection.
Put indicators to work instantly. Cyble delivers indicators of compromise straight into your SIEM, SOAR, and EDR through STIX/TAXII 2.1 feeds and REST APIs.
Cyble Vision: AI-Powered Threat Intelligence Platform
You can’t defend against what you can’t see.
Cyble Vision gives your team full visibility across the surface, deep, and dark web, uncovering leaked credentials, exposed assets, brand impersonation, and new cyber threats before adversaries can exploit them. By unifying attack surface management, dark web monitoring, and vulnerability intelligence in a single platform, Vision turns scattered external risk into clear, prioritized insight your team can act on immediately.

Cyble Blaze AI — AI-Native, Multi-Agent Cybersecurity
Threats move in milliseconds. Your defenses should too.
- Autonomous Detection
- Real-Time Response
- Multi-Agent Reasoning
- Zero Manual Triage
Key benefits of Cyble Threat Intelligence Platform
Comprehensive
Access extensive intelligence from surface, deep, and dark web sources to uncover, analyze, and respond to emerging threats in real time.
Precise
Gain unmatched visibility into threat actors and exploits, enabling prioritized, data-driven responses through advanced cyber threat intelligence Solution
Malware & Ransomware Intelligence
Monitor malware behavior, adversaries, and TTPs to detect, analyze, and neutralize attacks before they impact critical assets.
Opportune Intelligence Delivery
Leverage real-time, continuously updated intelligence for faster decision-making and automated mitigation through the Threat Intelligence Solution
Threat Library
Access a unified, searchable repository of structured and unstructured threat data for streamlined intelligence management.
Botnet Detection
Detect and disrupt botnet activities using AI-driven analytics and network anomaly detection to prevent large-scale attacks.
Why Choose Cyble Threat Intelligence solution?
Global Threat Coverage
Billions of indicators sourced from thousands of verified feeds.
Proactive Defense
Identify campaigns, zero-day exploits, and attacker tactics before impact.
Flexible Integrations
Connect seamlessly with SIEM, SOAR, and other SOC tools.
Trusted Expertise
Recognized among leading Threat Intelligence Companies for precision and reliability.
Actionable Insights
Transform data into intelligence that drives faster, better decisions.
How Cyble Threat Intelligence Solution Works
Gather
- The Cyble Cyber Threat Intelligence Solution collect data from the surface, deep, and dark web.
- Monitors covert communication channels and millions of global sources.
- Identifies emerging risks and active threat actors in real time.
Augment
- Uses AI-driven analytics to transform raw data into actionable intelligence.
- Provides a unified and contextual view of your organization’s threat landscape.
- Enhances decision-making through enriched cyber security threat intelligence insights.
Notify
- Integrates seamlessly with existing cyber threat intelligence solution and SIEM systems.
- Correlates Indicators of Compromise (IOCs) to detect exposed or vulnerable assets.
- Delivers instant alerts and reports for faster response and mitigation.
Threat Intelligence Platform & Solution Use Cases by Industry
Financial Services
Government & Defense
Monitor nation-state actors and safeguard critical assets with contextual Cyber Threat Intelligence Solution.
Healthcare
Prevent ransomware and data breaches by identifying exposure points early.
Retail & E-Commerce
Technology & Telecom
Defend against insider threats and APTs with advanced Threat Intelligence Solution capabilities.
Cyble’s cyber threat intelligence solution empower organizations to reduce risks, cut response times, and improve cyber resilience across industries.
Cyble Threat Intelligence vs Traditional Threat Intelligence
| What You Need | Cyble Threat Intelligence | Traditional Threat Intelligence |
|---|---|---|
| Scope | Threat intel, dark web monitoring, attack surface, brand, and third-party risk in one platform | Separate point tools, correlated by hand |
| Scale | 350B+ threat data points across the surface, deep, and dark web | Narrower, single-dimension coverage |
| Accuracy | AI-assisted collection, reviewed by analysts before it reaches you | Raw automated indicators, heavy on false positives |
| Next Steps | Each alert mapped to a recommended action: takedown, patch priority, or credential reset | Triage left entirely to your analysts |
| Remediation | Built-in takedowns with a 98.5% success rate | Findings stop at a report |
| Integration | 70+ enterprise integrations, plus STIX/TAXII 2.1 and REST APIs | Custom middleware to connect your stack |
Read the Analyst Reports Guiding Threat Intelligence Buying Decisions
Download the 2026 Gartner MQ Report
Works with your existing security stack


Not just feeds. Not just alerts.
Cyber Threat Intelligence
Data Sheets
Customer Reviews: Trusted by Global Leaders
From Fortune 500s,to government organizations, leading teams rely on Cyble’s solution to detect, respond, and stay ahead of evolving threats.
FAQs to get started with a Threat Intelligence Platform
What is a threat intelligence platform/solution?
What's the difference between a threat intelligence feed and a threat intelligence solution?
A threat intelligence feed provides raw indicators such as IPs, domains, and hashes, while a threat intelligence solution collects, correlates, analyzes, and prioritizes that data to deliver actionable insights. Cyble solutions can also support workflows such as dark web monitoring, takedowns, and SIEM integration, reducing the need for in-house tools and manual analysis.
How is Cyble's Threat Intelligence Solution different from competitors?
Cyble differentiates by unifying threat intelligence, dark web monitoring, attack surface management, brand protection, and third-party risk in a single platform (Cyble Vision), instead of requiring separate point tools that need to be manually correlated.
Its intelligence is AI-assisted for scale across deep and dark web sources, then reviewed by analysts before it reaches customers, which is intended to reduce the false-positive volume that raw automated feeds tend to produce. Native STIX/TAXII 2.1 support and REST APIs are built in for teams that need to feed findings directly into existing SIEM, SOAR, or ticketing workflows.
What integrations should a CTI platform support?
A CTI platform should support REST APIs and STIX/TAXII 2.1 for standardized exchange, plus pre-built connectors for common SIEM platforms (e.g., Splunk, Microsoft Sentinel, QRadar) so indicators flow into detection and response workflows without custom middleware. STIX/TAXII support alone doesn’t guarantee smooth integration — confirm a pre-built connector exists for your specific SIEM before assuming API access is sufficient.
What should a CTI platform proof of concept test?
A CTI POC should test IOC/IOA relevance to your industry, false-positive rate against known-good indicators, SIEM/SOAR/EDR integration, dark web and leaked-credential coverage for your own domains, and analyst turnaround time on custom requests — using live data over a 2–4 week window, not a static demo. A POC scoped to your own attack surface reveals far more than a vendor dashboard walkthrough.
How should a CTI vendor shortlist be built?
Buyers should evaluate vendors against five criteria — dark-web and closed-source coverage, SIEM/SOAR/EDR integration, actionability (built-in remediation vs. feeds only), analyst support model, and pricing transparency — and run a proof of concept before committing, rather than relying on analyst rankings alone.
When does a company need a full CTI platform versus a narrower credential-monitoring tool?
A full CTI platform is usually more than a team needs if the only concern is employee credential exposure — a dedicated dark web monitoring module covers that need at lower cost. Teams should reconsider once requirements expand to IOC feeds for SIEM enrichment, vulnerability prioritization, or brand/executive protection. Cyble Vision is priced modularly, so a team can start with one module and expand without switching platforms.
What should be checked in a CTI platform contract before signing?
Before signing, buyers should review module bundling, data/query volume caps, analyst seat costs, API limits, and renewal/price-lock clauses — and confirm what happens if usage exceeds contracted limits mid-term. A platform that looks affordable at signing can become expensive once added modules, seats, or data sources require upgrades.
- Module bundling — whether dark web monitoring, EASM, and brand protection are included or billed separately
- Data/query caps — what triggers an overage charge
- Seat costs — price of adding analysts mid-contract
- API limits — relevant for SIEM/SOAR integration
- Renewal clauses — whether year-two pricing is locked
How much do cyber threat intelligence solution cost?
The cost of cyber threat intelligence solutions varies based on factors such as intelligence coverage, monitored assets, users, integrations, and included capabilities like dark web monitoring or EASM. Businesses should consider a solution’s overall value and operational efficiency, not just its subscription price.
How can CISOs measure whether threat intelligence is reducing risk?
CISOs should measure operational impact — Mean Time to Detect, Mean Time to Respond, critical vulnerabilities remediated, and analyst time saved — rather than the raw number of indicators collected, since volume metrics don’t demonstrate whether intelligence is actually reducing exposure.
Do Small Businesses Need Threat Intelligence Solution?
Not every small business needs an enterprise-grade solution, but threat intelligence can help SMBs identify risks such as leaked credentials, dark web exposure, phishing, and emerging threats. For businesses with limited security resources, a lightweight or managed solution like Cyble can provide actionable threat intelligence without requiring an in-house CTI team.
What are the different types of threat intelligence?
Cyber threat intelligence is generally organized into three core types — strategic, operational, and tactical — with many vendors and analysts adding technical as a fourth category for machine-readable indicators.
- Strategic: high-level trends and business risk, written for executives and board members.
- Operational: campaign tracking and adversary motivation, used to understand the “who” and “why” behind an attack.
- Tactical: adversary tactics, techniques, and procedures (TTPs), used by analysts to anticipate attacker behavior.
- Technical: indicators of compromise (IOCs) such as malicious IPs, file hashes, and domains, consumed directly by security tools.
What is Threat Intelligence Services?
Threat intelligence services are managed offerings in which a vendor collects, analyzes, and delivers curated information about active and emerging cyber threats — such as threat actor activity, malware, leaked credentials, and exposed vulnerabilities — so a security team can act on it without building that capability in-house.
Unlike a raw data feed, these services are typically backed by analysts who validate findings, add context, and tailor reporting to a client’s specific assets, industry, and risk profile. Cyble delivers this as Cyble Vision, combining automated collection with analyst-reviewed intelligence available via dashboard, API, or STIX/TAXII feed.
What are the 3 Ps of threat intelligence?
The “3 Ps of threat intelligence” is most commonly defined as Proactive, Predictive, and Preventive: proactively hunting for threats before they’re flagged, predicting likely attacks based on adversary patterns, and using that insight to prevent incidents before they cause damage.
The term isn’t formally standardized, though — some sources use Predict, Prevent, Protect, and others apply it to program resources (People, Process, Products) rather than intelligence approaches. Whichever version is used, the underlying goal is the same: shifting security from reactive to anticipatory.
What is cyber threat intelligence (CTI)?
Cyber threat intelligence (CTI) is evidence-based knowledge about existing or emerging cyber threats — including context, mechanisms, indicators, and recommended action — that helps organizations make informed security decisions. It differs from raw threat data by adding analysis: CTI doesn’t just flag that an IP address is malicious, it explains who’s behind the activity, why it matters to a specific organization, and what to do about it. CTI typically spans three levels — strategic (executive-level risk trends for budget and planning), operational (threat-actor and campaign context for security managers), and tactical (specific indicators of compromise for blocking) — each serving a different audience within a security program.
What is the threat intelligence process?
The threat intelligence process, often called the threat intelligence lifecycle, is the structured workflow that turns raw data into actionable intelligence. It runs through five stages — direction, collection, processing, analysis, and dissemination — with feedback looping back to refine the next cycle.
Direction sets the priority intelligence requirements based on business risk; collection and processing gather and normalize the data; analysis adds context and assesses relevance; dissemination delivers findings to the right stakeholders in a usable format.
What are the steps of the intelligence cycle?
The intelligence cycle has five core steps that repeat continuously as priorities and threats change.
- Direction/Planning — define intelligence requirements tied to business risk.
- Collection — gather data from internal telemetry, open sources, and dark web monitoring.
- Processing — normalize and filter raw data into a usable format.
- Analysis — correlate signals, assess relevance, and identify what matters most.
- Dissemination and feedback — deliver findings to stakeholders and use their input to refine the next cycle.
What are the 5 phases of NIST?
The NIST Cybersecurity Framework organizes its guidance into five core functions: Identify, Protect, Detect, Respond, and Recover. Each function groups a set of outcome-driven activities an organization should perform to manage cyber risk.
- Identify — inventory assets, data, and risks.
- Protect — implement safeguards such as access controls and training.
- Detect — build the capability to spot security events quickly.
- Respond — contain and act on detected incidents.
- Recover — restore capabilities and services after an incident.
What are the three key elements of threat intelligence?
Threat intelligence is generally built from three key elements: evidence, context, and mechanism. Evidence means the information is backed by real data and observation, not speculation; context explains why, when, and where a threat typically occurs; and mechanism describes how it actually works — the tactics, techniques, and procedures (TTPs) behind it.
Some frameworks describe this triad differently — as timeliness, relevance, and accuracy — but the intent is the same: intelligence that’s current, specific to the organization, and verified is what makes it actionable rather than just informational.
What is third-party threat intelligence?
Third-party threat intelligence is intelligence focused specifically on risks introduced by an organization’s vendors, suppliers, and partners — rather than threats aimed directly at the organization itself. It covers things like a vendor’s exposed credentials, breach history, dark web mentions, and known vulnerabilities in their infrastructure.
This differs from standard CTI because the assets being monitored aren’t owned by the organization, so intelligence has to be gathered externally. Cyble’s third-party risk management module correlates this vendor-side intelligence with an organization’s own exposure to flag which vendor risks are most likely to affect it directly.
Who are Threat Intelligence Providers?
Threat intelligence providers are the organizations that supply the data, analysis, or platforms security teams use to understand and respond to cyber threats. They generally fall into four categories.
- Commercial CTI platforms — vendors like Cyble that combine automated collection with analyst-validated intelligence, delivered through a platform, API, or managed service.
- Open-source and community feeds — projects such as MISP or AlienVault OTX that share indicators freely, usually with less curation.
- Information Sharing and Analysis Centers (ISACs/ISAOs) — industry-specific groups that share sector-relevant threat data among members.
- Government and national agencies — bodies such as CISA that publish advisories and indicators for public use.
Which Cyber Threat Intelligence Service is the best?
There’s no single “best” CTI service — the right choice depends on an organization’s asset visibility needs, existing SIEM/SOAR stack, analyst capacity, and budget. The evaluation should center on source coverage, false-positive rate, integration depth, and whether findings come with enough context to act on.
Cyble Vision is built to compete on those specific criteria — combining dark web and surface web monitoring, STIX/TAXII-based integrations, and analyst-reviewed findings in one platform rather than requiring separate tools for each. Whether it’s the right fit still depends on running it against an organization’s own environment in a proof of concept.
What differentiates modern CTI platforms from legacy, feeds-only vendors?
Legacy, feeds-only vendors typically deliver raw indicators and leave correlation, prioritization, and remediation to the buyer’s own team; modern AI-native platforms correlate, prioritize, and route findings into remediation workflows automatically. Cyble Vision, built on Cyble’s Blaze AI reasoning engine, maps each alert to a recommended action — a takedown request, a patch priority, or a credential reset — rather than leaving triage entirely to the analyst. Cyble was named a Challenger in the inaugural 2026 Gartner® Magic Quadrant™ for Cyberthreat Intelligence Technologies, one of two Challengers among 17 evaluated vendors.
Ready to See Cyble Threat Intelligence Solution in Action?
Request a personalized demo to experience how Cyble’s Threat Intelligence Solution enhance your cybersecurity strategy, integrate seamlessly with your tools, and help you stay ahead of evolving threats.