
Industry-Leading
Attack Surface Management Solution
See Every Risk. Secure Every Asset.
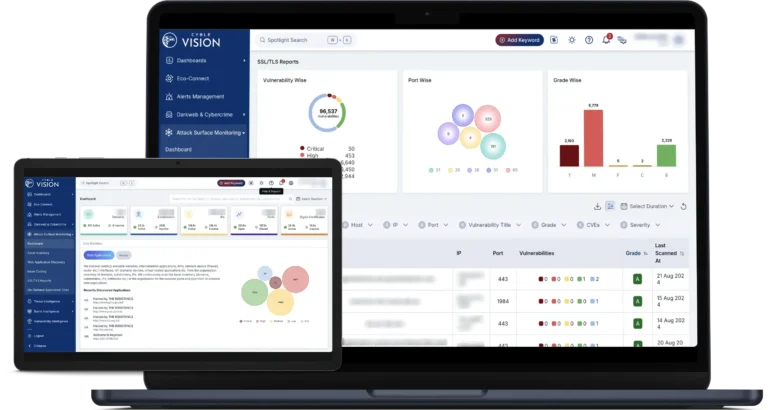
The Cyble Attack Surface Management Solution discovers, and tracks exposed digital assets while also providing continuous visibility across web and mobile apps, cloud systems, domains, email servers, IoT devices, and public repositories.
Cyble Named a Challenger in the 2026 Gartner® Magic Quadrant™ for Cyberthreat Intelligence Technologies
What is Cyble Attack Surface Management Solution?
See More. Secure More.
Cyble Attack Surface Management Solution helps organizations discover, monitor, and protect their external digital assets. It provides continuous visibility across domains, websites, web and mobile applications, cloud environments, email servers, IoT devices, and public code repositories.
By continuously monitoring your attack surface, Cyble identifies exposed assets, security weaknesses, and potential risks in real time. Security teams can prioritize actionable findings, investigate exposures, and take faster steps to reduce their organization’s risk.
With a unified view of your digital footprint, Cyble makes it easier to identify unknown assets, detect emerging threats, and maintain a stronger security posture as your attack surface evolves.
What are the Different Types of Attack Surfaces?
- External Attack Surface
Internet-facing domains, IP addresses, open ports, and exposed services.
- Digital Attack Surface
Websites, web and mobile apps, APIs, email servers, and code repositories.
- Cloud Attack Surface
Cloud infrastructure, storage, and services with potential misconfigurations.
- Internal Attack Surface
Internal networks, endpoints, servers, and applications.
- Third-Party Attack Surface
Vendor systems, partner integrations, and supply chain dependencies.
- Shadow IT Attack Surface
Unauthorized applications, unknown cloud assets, and forgotten development environments.
- IoT and OT Attack Surface
Connected devices and industrial systems vulnerable to exploitation.
See Your Attack Surface the Way Attackers Do
Continuous external scanning from the attacker's perspective — mapping every exposed asset, open port, misconfigured service, and leaked credential visible on the public internet.
Deep visibility into your supply chain and third-party dependencies — so you control your risk surface beyond your own perimeter, including vendor exposures that could become your breach.
Shadow IT is Your Blind Spot
Unknown cloud instances, unsanctioned SaaS tools, and forgotten dev environments — Cyble discovers and maps assets your IT team doesn’t even know exist, before attackers find them first.
Common shadow IT risks Cyble uncovers:
- Unknown cloud instances (AWS, Azure, GCP) spun up outside IT oversight
- Unsanctioned SaaS tools connected to corporate credentials
- Forgotten development and staging environments left exposed
- Personal devices and unapproved apps accessing corporate data
No Scheduled Scans. No Blind Windows.
Continuous external attack surface scanning
Most ASM Tools Show You What's Exposed. Cyble Shows You What's Being Targeted.
| Typical ASM Tools | Cyble ASM |
|---|---|
| × Show asset exposure | ✓ Shows what’s exposed AND what’s actively targeted |
| × List vulnerabilities by CVSS score | ✓ Layers adversary context on top of CVSS |
| × No dark web correlation | ✓ Live dark web signal integration |
| × No adversary intent signals | ✓ Real-time adversary tracking |
Every Layer of Your External Attack Surface. Automatically.
Full enumeration and monitoring of subdomains, including orphaned and forgotten assets.
AWS, Azure, and GCP instances, storage buckets, and services exposed to the internet.
Undocumented, deprecated, or misconfigured API endpoints accessible externally.
Vendors and supply chain partners whose exposure could become your risk.
Unknown or unsanctioned apps, tools, and cloud services not managed by your IT team.
Newly opened ports and unexpected running services across your IP ranges.
Expiry alerts, weak cipher detection, and certificate mis-issuance monitoring.
Credentials from your domain appearing in breach dumps and dark web markets.
Not Every Exposure is a Crisis.
| CVSS Alone | Cyble AI Scoring |
|---|---|
| × Technical severity only | ✓ CVSS + adversary context |
| × No business context | ✓ Asset criticality weighting |
| × No adversary signal | ✓ Live dark web signal overlay |
| × Leaves teams chasing low-risk findings | ✓ Fix-first guidance for your team |
One Platform. Complete Picture.
Cyble ASM is natively integrated with Cyble’s Threat Intelligence Platform — so every exposed asset is automatically enriched with threat actor context, dark web signals, and active exploit data.
What native TIP integration delivers:
- Every discovered asset automatically enriched with threat actor intelligence
- Dark web chatter correlated directly with your exposed assets
- Active exploit data surfaced against your specific exposure profile
- Single pane of glass: ASM + TIP + dark web monitoring in one workflow
Built for Regulated Environments.
Continuous asset discovery and exposure monitoring supports Zero Trust network architecture initiatives.
Aligns with Continuous Threat Exposure Management frameworks for proactive risk reduction.
Meets requirements for continuous risk management and attack surface monitoring under EU NIS2 regulation.
Built-in dashboards and compliance reports for governance, audit committees, and regulatory submissions.
Key benefits of Attack Surface Management Solution
Asset Discovery
Map all internet-facing assets in one view to improve security investigations and monitoring.
Actionable Context
Real-time and historical insights across on-prem and cloud assets for smarter decision-making.
Application Security Scanning
Automatically detect XSS, SQL Injection, and other app vulnerabilities from the outside in.
Code Repository Analysis
AI-driven scans to uncover insecure code and reduce development risks.
Cloud Storage Analysis
Find exposed data or misconfigured cloud assets before attackers do.
Vulnerability Management
Prioritize and fix weaknesses with full context on asset-level risks.
IP Risk Scoring
Assess malicious activity linked to IPs with intelligence-based scoring.
New Port Discovery
Detect newly opened ports to reduce unexpected entry points.
SSL Expiry Alerts
Monitor certificate expiry to prevent security lapses.
Domain Expiry Alerts
Track domain renewals to avoid downtime or takeover risks.
Why Choose Cyble Attack Surface Management Solution?
Uncover Risks. Protect Every Asset.
Comprehensive Visibility
Uncovers and monitors all digital assets — including shadow IT and supply chain exposures.
Real-Time Threat Detection
Spot vulnerabilities across web, mobile, cloud, domains, email, IoT, and code repositories instantly.
Proactive Protection
Attack Surface Management Solution safeguard your assets before threats strike.
Continuous Monitoring
24/7 security and compliance monitoring — no scheduled scans, no blind windows.
Threat-Intel-Linked
Only Cyble links exposed assets with dark web signals and adversary tracking in a single platform.
Unified Platform
ASM + TIP + dark web monitoring from a single platform. One dashboard. Complete picture.
Compliance-Ready
Aligns with Zero Trust, CTEM, and NIS2 Article 21 requirements out of the box.
How Cyble Attack Surface Management Solution Turns Visibility into Action ?
Eliminate Digital Risks
Identify internet-exposed assets before they become hacker entry points. Strengthen defences with continuous Attack Surface Management Solution.
Eliminate Blind Spots
Use AI and NLP to analyze thousands of posts for leaked data and attack discussions. Uncover hidden threats before they escalate.
Detect and Respond
Assess the impact of breaches or cloud misconfigurations. Take swift action with Attack Surface Management Solution and managed services.
Industry Use Cases & Customer Impact
How Our Solution Work for You
Financial Services
Healthcare
Retail & E-Commerce
Manufacturing & Critical Infrastructure
Technology & SaaS Providers
Frequently Asked Questions About Attack Surface Management Solution
What is attack surface management (ASM)?
Attack surface management (ASM) is the continuous process of discovering, assessing, and prioritizing an organization’s internet-facing assets — domains, cloud instances, APIs, web applications, and more — to reduce the risk of exposure attackers could exploit. It’s distinct from a one-time security assessment: ASM runs continuously so newly exposed assets (a forgotten subdomain, a misconfigured cloud bucket) are flagged as they appear, not at the next scheduled scan. External attack surface management (EASM) specifically refers to doing this from an outside-in, attacker’s-eye view using public data, without requiring internal network access.
What is Attack Surface monitoring, and how does it work?
Attack surface monitoring is the continuous discovery and tracking of an organization’s internet-facing assets to detect new, changed, or misconfigured exposures as they appear, rather than relying on periodic audits. It works by combining passive reconnaissance — DNS records, certificate transparency logs, WHOIS data, and public cloud metadata — with active scanning to build a live asset inventory and flag risk changes in near real time. Cyble Vision runs this discovery-and-scan cycle continuously, alerting teams the same day a new subdomain, open port, or exposed cloud bucket surfaces.
What types of assets does ASM cover?
ASM covers all internet-facing assets, including domains and subdomains, IP address ranges, cloud workloads across AWS, Azure, and GCP, web applications and APIs, SSL/TLS certificates, exposed databases and admin panels, DNS records, and third-party or vendor-connected systems. Comprehensive ASM platforms also surface leaked credentials and code repository exposures tied to those assets, since a leaked API key or password is effectively part of the attack surface too. Cyble Vision maps this full range of asset types and keeps the inventory current as infrastructure changes.
What is External Attack Surface Management?
External Attack Surface Management (EASM) is the practice of continuously discovering, inventorying, and assessing all internet-facing assets an organization owns — including unknown or unmanaged ones — from the perspective of an outside attacker. Unlike internal vulnerability management, EASM starts with no assumed asset list; it finds what’s actually exposed to the internet by scanning the same way an attacker would reconnoiter a target. Cyble Vision’s EASM module continuously discovers domains, IPs, cloud assets, and exposed services tied to an organization, without requiring agents.
How to mitigate Attack Surface risks?
Mitigating attack surface risk starts with maintaining a complete, current asset inventory, since you can’t fix exposure you don’t know about. From there, the standard steps are: patch or reconfigure vulnerable assets, decommission unused or forgotten systems, enforce least-privilege access and multi-factor authentication on exposed services, and monitor continuously for new exposures rather than relying on periodic reviews. Combining this with threat intelligence, knowing which of your exposures are being actively targeted, lets teams mitigate the highest-risk issues first instead of working through a flat list.
What does attack surface management actually do?
What should an Attack Surface Management solution do?
An attack surface is the entire set of potential entry points into an organization’s systems, while an attack vector is the specific technique used to exploit one of those entry points. Put simply, the attack surface is the “where” and the attack vector is the “how” — an exposed VPN endpoint is part of the attack surface; using stolen credentials to log into it is the attack vector. Reducing the attack surface, meaning fewer exposed assets, limits how many vectors are available to an attacker in the first place.
How does Attack Surface Management help prevent cyberattacks?
What's the difference between attack surface management and vulnerability management?
What assets can an EASM platform discover?
An EASM platform can discover internet-facing assets across six categories: domains and subdomains, web and mobile applications, cloud instances and storage, APIs, IoT/OT devices, and public code repositories — including third-party and subsidiary infrastructure connected to the organization. Coverage across all six matters because attackers don’t limit reconnaissance to a primary domain.
Customer Reviews: Trusted by Global Leaders
From Fortune 500s,to government organizations, leading teams rely on Cyble’s solution to detect, respond, and stay ahead of evolving threats.
Manager, IT Security & Risk Management - Real Estate
IT Services Associate - IT Services
CISO – Manufacturing
Deputy General Manager – Consumer Goods
IT Services Associate - Miscellaneous
Software Developer - IT Services
Ready to See Cyble Attack Surface Management Solution in Action?

Attack Surface Management
Data Sheets